Separate Administration from Vault Access
Devolutions Server 2026.3 adds granular roles separating workspace administration from vault content access, helping teams limit permissions to each user’s needs.
Devolutions Server is a secure, self-hosted solution designed to centralize and manage privileged access, credentials, and remote connections for organizations. It enables IT professionals and software developers to securely store and share sensitive data like passwords, API keys, and remote session details within a centralized vault, with robust user access controls and role-based permissions. Devolutions Server integrates with existing infrastructure, supports multi-factor authentication, and provides auditing and logging capabilities to track activities and help support compliance with security policies.
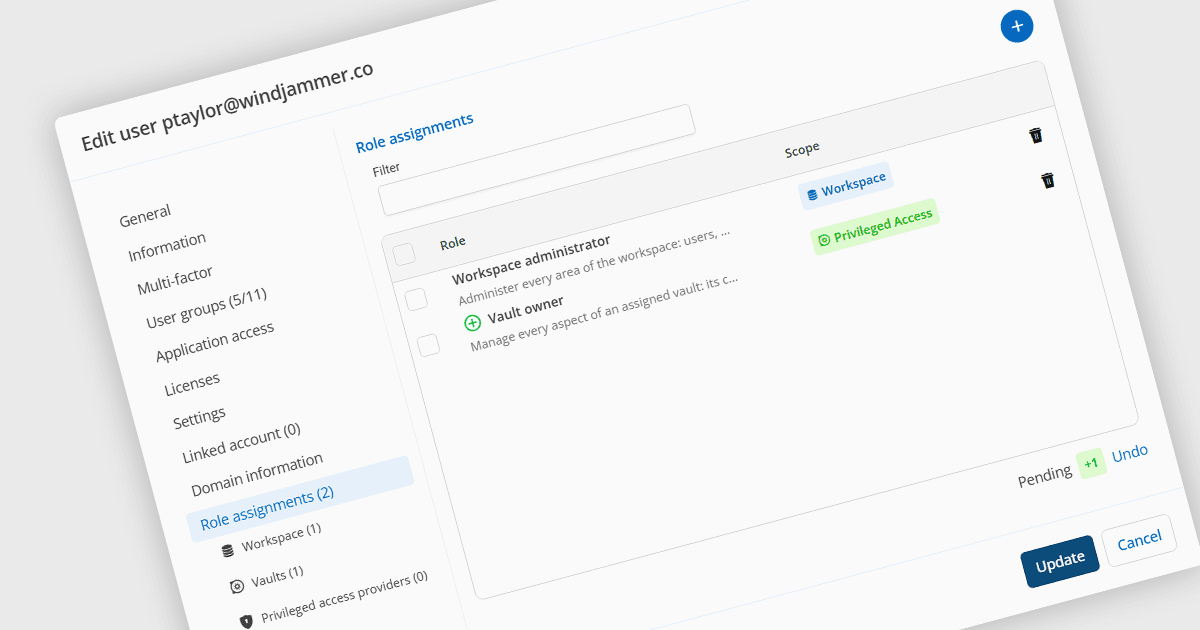
Devolutions Server 2026.3 introduces a role model that helps teams apply least-privilege security by assigning permissions according to job responsibilities. Workspace management and vault content access are handled separately: the Workspace administrator role permits administration of licenses, user accounts, vaults, and templates without automatically granting access to credentials or other stored entries. The Auditor role allows read-only review of administration and reports within its assigned scope without granting permission to open vault entries, while activity logs are accessible through the separate Workspace log viewer role. During an upgrade, existing administrators receive the Workspace owner role, preserving their previous access unless their role assignments are subsequently changed.
For a full list of what's new in 2026.3, see our release notes.
Devolutions Server is available as part of the Devolutions Starter Pack for teams of up to five users, which is licensed per user and offered as an annual subscription. See our Devolutions Server licensing page for full details.
To find out more, visit our Devolutions Server product page.